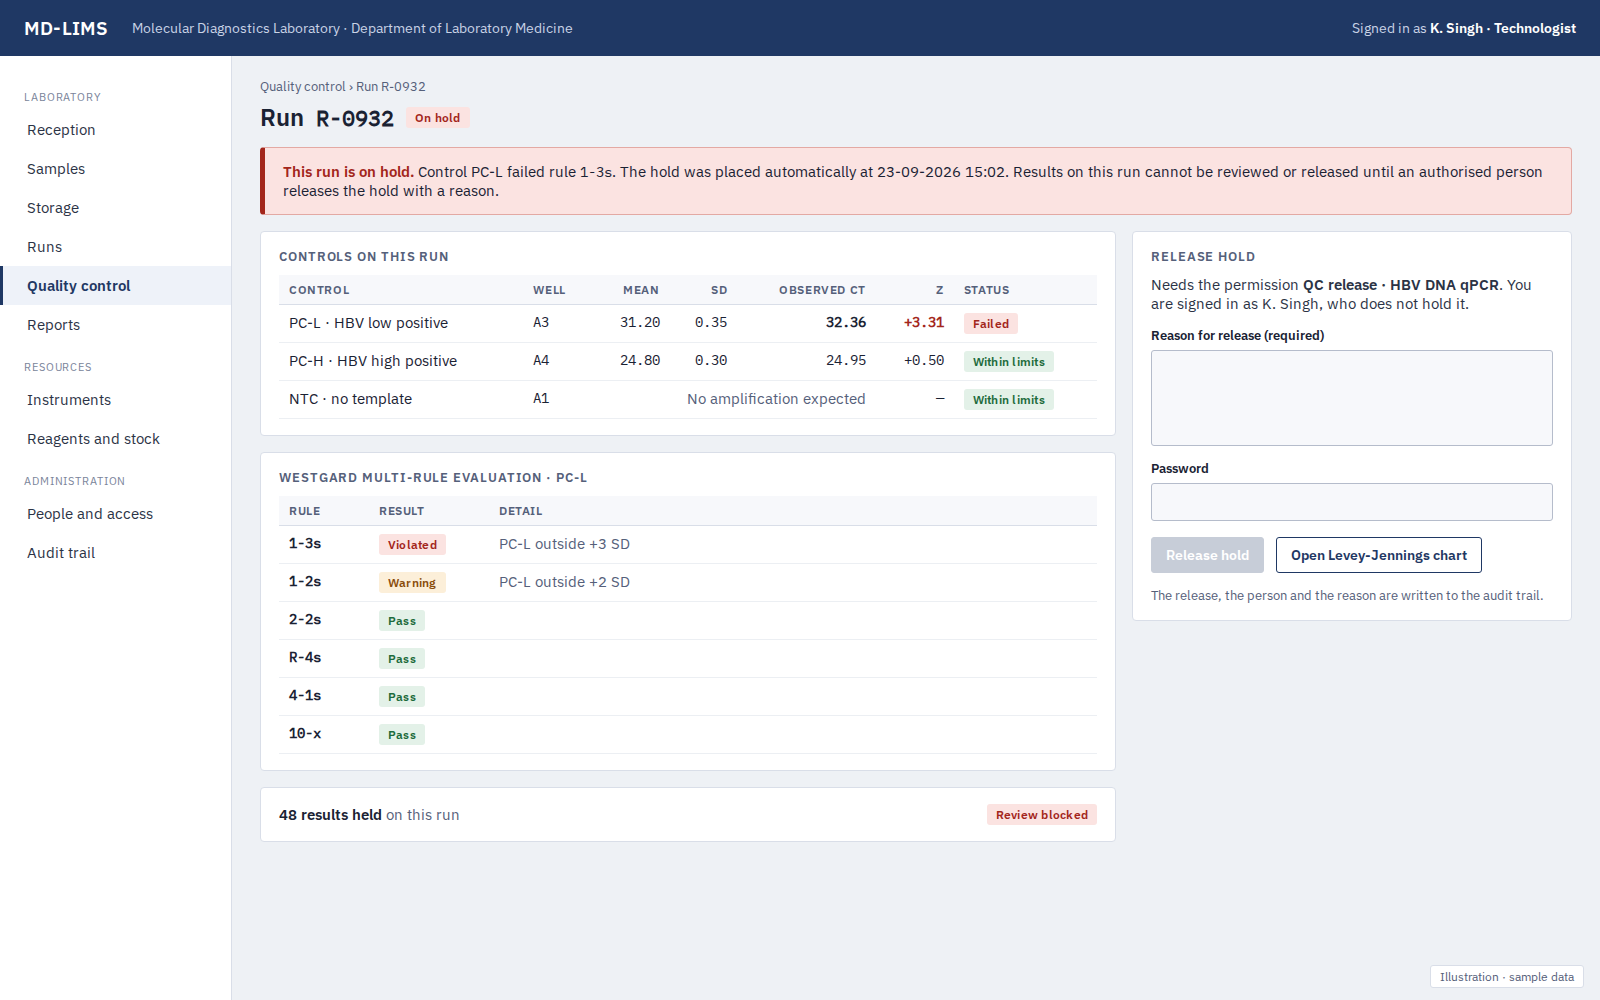
Security enforced by the database, not by the screens.
Access rules are written into PostgreSQL as row-level security and enforced by the database itself, not by filters in the application’s queries. The account the application connects with owns nothing and cannot bypass them. The system administrator holds no laboratory permission and cannot read patient results.